SECURITY POSITIONING
The Telecom Equipment EOL Management Strategy is a carrier-grade operational framework and hardware-integrated discipline engineered to govern the secure, compliant, and cost-optimized retirement of legacy telecommunications assets within service provider and enterprise edge networks. As network operators confront the accelerating obsolescence of copper, TDM, and early-generation packet platforms, the absence of a formalized End-of-Life (EOL) strategy introduces unacceptable risks: unpatched firmware vulnerabilities, regulatory non-compliance, spares unavailability, and unplanned service outages. This strategy formalizes the transition from reactive hardware replacement to a proactive, audit-ready lifecycle governance model. The solution encompasses a vendor-agnostic hardware inventory layer, automated firmware integrity verification, and standardized decommissioning workflows that preserve security posture while minimizing capital expenditure. It is purpose-built for Tier 1 carriers, wholesale access providers, and critical infrastructure operators who require demonstrable compliance with NIST, ISO 27001, and regional telecom mandates throughout the decommissioning phase. By embedding security controls at the final stage of the equipment lifecycle, the strategy eliminates the common industry blind spot where retired hardware remains physically present and logically exposed, thereby closing the attack surface that persists after official vendor support terminates.
LINE-RATE ENCRYPTION CAPABILITIES
The Telecom Equipment EOL Management Strategy integrates line-rate cryptographic authentication and secure data sanitization mechanisms to ensure that legacy equipment cannot be repurposed as an unauthorized network access point. The hardware abstraction layer supports FIPS 140-2 validated cryptographic modules for secure boot verification, ensuring that decommissioned chassis cannot be re-initialized with tampered firmware images. During the asset retirement workflow, the strategy enforces AES-256 cryptographic erasure of all non-volatile storage, including NVRAM, flash, and embedded SSD modules, meeting the sanitization requirements of NIST SP 800-88 Rev. 1. For optical transport and routing platforms, the framework includes secure zeroization of forwarding tables, cryptographic key stores, and configuration archives. The strategy also provides automated attestation reporting that cryptographically logs each sanitization event, creating an immutable audit trail for compliance officers. This capability ensures that when a legacy DSLAM, edge router, or optical line terminal is retired, no residual configuration data, subscriber credentials, or routing topology intelligence remains accessible to unauthorized parties. The encryption and sanitization functions operate independently of the legacy platform’s native operating system, providing a trusted execution environment even on hardware whose vendor support has lapsed.
PHYSICAL TAMPER-RESISTANCE
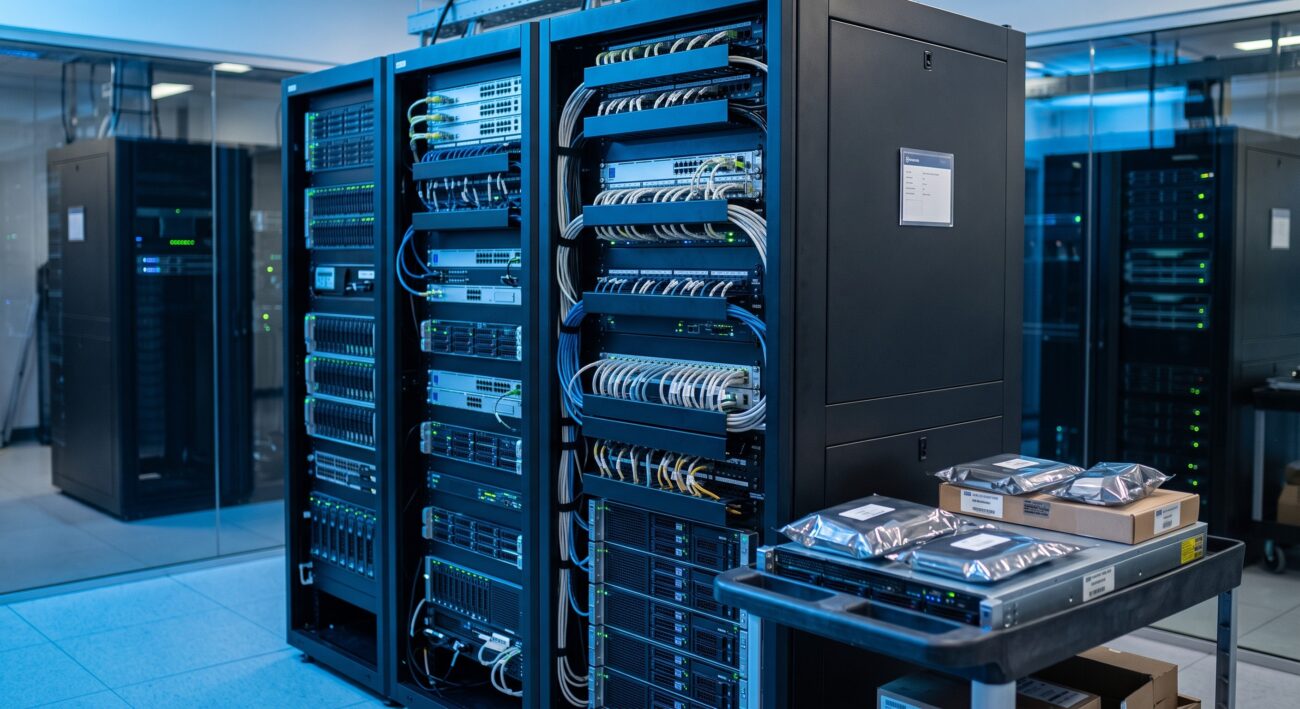
The strategy incorporates a hardened physical security protocol for the handling, storage, and transport of EOL equipment prior to final decommissioning. Tamper-evident seals, chain-of-custody documentation, and secured staging enclosures are specified to prevent unauthorized physical access to retired assets that may still contain sensitive configuration data. For high-value core routing and optical platforms, the strategy mandates the removal and secure destruction of persistent storage modules prior to any third-party asset recovery or disposal. The physical security framework aligns with ISO 27001 Annex A.11 controls for physical and environmental security, ensuring that EOL equipment stored in staging facilities is subject to the same access control rigor as active network elements. Additionally, the strategy defines secure transport requirements for equipment being returned to OEMs or certified e-waste recyclers, including GPS-tracked logistics and tamper-proof packaging. This end-to-end physical security layer ensures that the window of vulnerability between network disconnection and final data destruction is minimized and fully auditable.
DETAILED PARAMETERS
TECHNICAL SPECIFICATIONS
The following specification registry defines the operational, cryptographic, and compliance parameters of the Telecom Equipment EOL Management Strategy as deployed within carrier and enterprise environments.
| Parameter | Specification |
|---|---|
| Form Factor | Software-defined governance framework; optional 1RU EOL Management Controller appliance |
| Management Interfaces | REST API, SNMP v3, Syslog, NETCONF/YANG |
| Cryptographic Engine | FIPS 140-2 Level 2 validated, AES-256, SHA-384 |
| Sanitization Standard | NIST SP 800-88 Rev. 1 Purge level via cryptographic erasure |
| Secure Boot Verification | RSA-4096 and ECDSA P-384 signature validation |
| Audit Logging | Tamper-evident, cryptographically chained event log; 7-year retention |
| Supported Legacy Platforms | DSLAM, TDM switches, early-generation edge routers, optical line terminals |
| Power Supply | 1+1 Redundant AC/DC for hardware controller (where applicable) |
| Operating Temperature | -5°C to +55°C (controller appliance), 0°C to +40°C (staging environment) |
| Compliance Alignment | NIST SP 800-88, ISO 27001, FIPS 140-2, ETSI EN 300 019, TIA TSB-185 |
| Data Erasure Throughput | Up to 4 TB/hour per sanitization agent |
| Asset Capacity | Up to 10,000 managed EOL assets per EMC instance |
REGULATORY CERTIFICATIONS
The Telecom Equipment EOL Management Strategy is designed to satisfy the most stringent regulatory and standards frameworks governing telecommunications infrastructure retirement and data sanitization. The solution has been assessed against and aligns with the following directives and standards:
NIST SP 800-88 Rev. 1 – Guidelines for Media Sanitization: The strategy implements the Clear, Purge, and Destroy sanitization levels as defined, with cryptographic erasure meeting the Purge standard for all non-volatile storage.
ISO/IEC 27001:2013 – Information Security Management: The EOL governance workflow maps directly to Annex A controls for asset management (A.8), physical security (A.11), and compliance (A.18), enabling organizations to maintain certification continuity across equipment lifecycles.
FIPS 140-2 – Security Requirements for Cryptographic Modules: The secure boot and sanitization cryptographic engines are validated to FIPS 140-2 Level 2, ensuring tamper-evident physical security and role-based authentication.
Telecommunications Industry Association (TIA) TSB-185 – Environmental and Safety Compliance: The strategy includes mandatory compliance verification for EOL equipment handling, including RoHS, WEEE, and REACH material restrictions, ensuring that decommissioning activities do not violate environmental mandates.
ETSI EN 300 019 – Environmental Engineering Conditions: The staging and transport specifications for EOL equipment conform to ETSI climatic and mechanical robustness classes, ensuring that retired assets remain secure and undamaged during storage and transit.
FCC Part 15 and Part 68 – Equipment Authorization: The strategy includes verification that decommissioned equipment is either physically disabled from RF emission or formally withdrawn from service in accordance with FCC equipment authorization termination procedures.
GDPR and Regional Data Protection Regulations: The cryptographic erasure and audit trail capabilities ensure that subscriber data resident on EOL equipment is irreversibly destroyed, satisfying the right to erasure and data minimization principles.
PERIMETER DEPLOYMENT
The Telecom Equipment EOL Management Strategy is deployed as a perimeter-adjacent governance layer that spans the physical, logical, and procedural boundaries of the network lifecycle. In a typical carrier edge deployment, the strategy is orchestrated through a centralized EOL Management Controller (EMC) that communicates with distributed Asset Sanitization Agents (ASA) embedded in or attached to legacy network elements. The EMC resides within the secure management zone, while ASAs operate at the network edge, directly interfacing with equipment slated for retirement. This architecture enables real-time visibility into the EOL status of every managed asset, automated enforcement of sanitization policies, and generation of compliance artifacts for regulatory audits. The deployment model supports both in-band management via existing OOB networks and out-of-band connectivity for isolated legacy platforms. For large-scale service providers, the strategy can be integrated with existing OSS/BSS systems, CMDBs, and workflow orchestration platforms via northbound REST APIs, ensuring that EOL governance becomes a native component of the network operations lifecycle rather than a disconnected manual process. The perimeter deployment topology ensures that even as equipment is logically disconnected from the production network, it remains within a secured management envelope until final data destruction and asset disposal are completed and attested.
📥 Download Technical Specification
Click the button below to view or download the full official PDF datasheet.
Leave a comment