
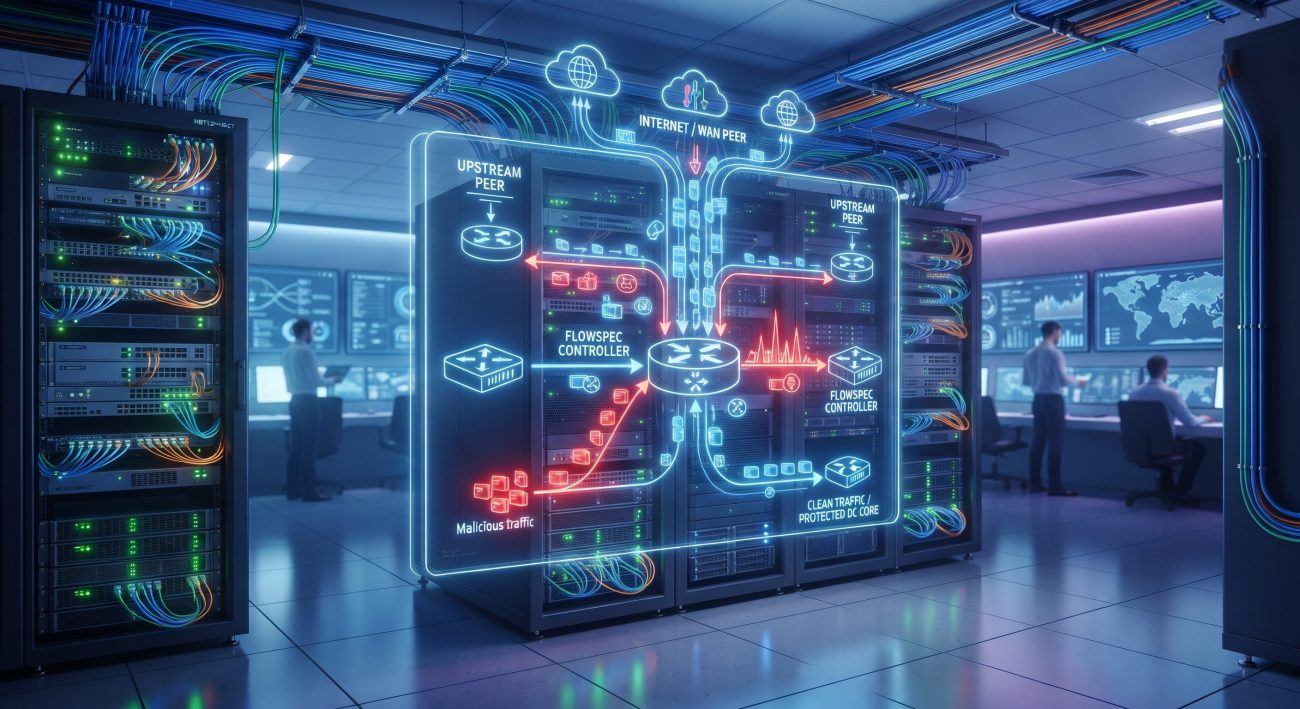
The SLA Imperative: Why Edge Scrubbing Reliability Defines Modern DDoS Defense
In the contemporary threat landscape, volumetric and multi-vector DDoS attacks are no longer measured merely in gigabits per second but in business continuity risk. For tier-1 carriers and large-scale enterprises, the decision to deploy BGP Flowspec (RFC 5575) at the edge is not merely a feature upgrade; it is an architectural commitment to sub-second mitigation latency and carrier-grade availability. While legacy RTBH (Remotely Triggered Black Hole) offers a blunt instrument that sacrifices the target, FlowSpec introduces surgical precision. However, with this precision comes a critical dependency on control-plane stability and hardware ASIC resilience. A scrubbing architecture is only as effective as its weakest link in the failover chain. This analysis evaluates the operational reliability of FlowSpec-driven scrubbing, focusing on MTBF (Mean Time Between Failures), dual-engine redundancy, and the rigorous standards required to maintain 99.999% availability under sustained attack loads exceeding 40 Gbps.
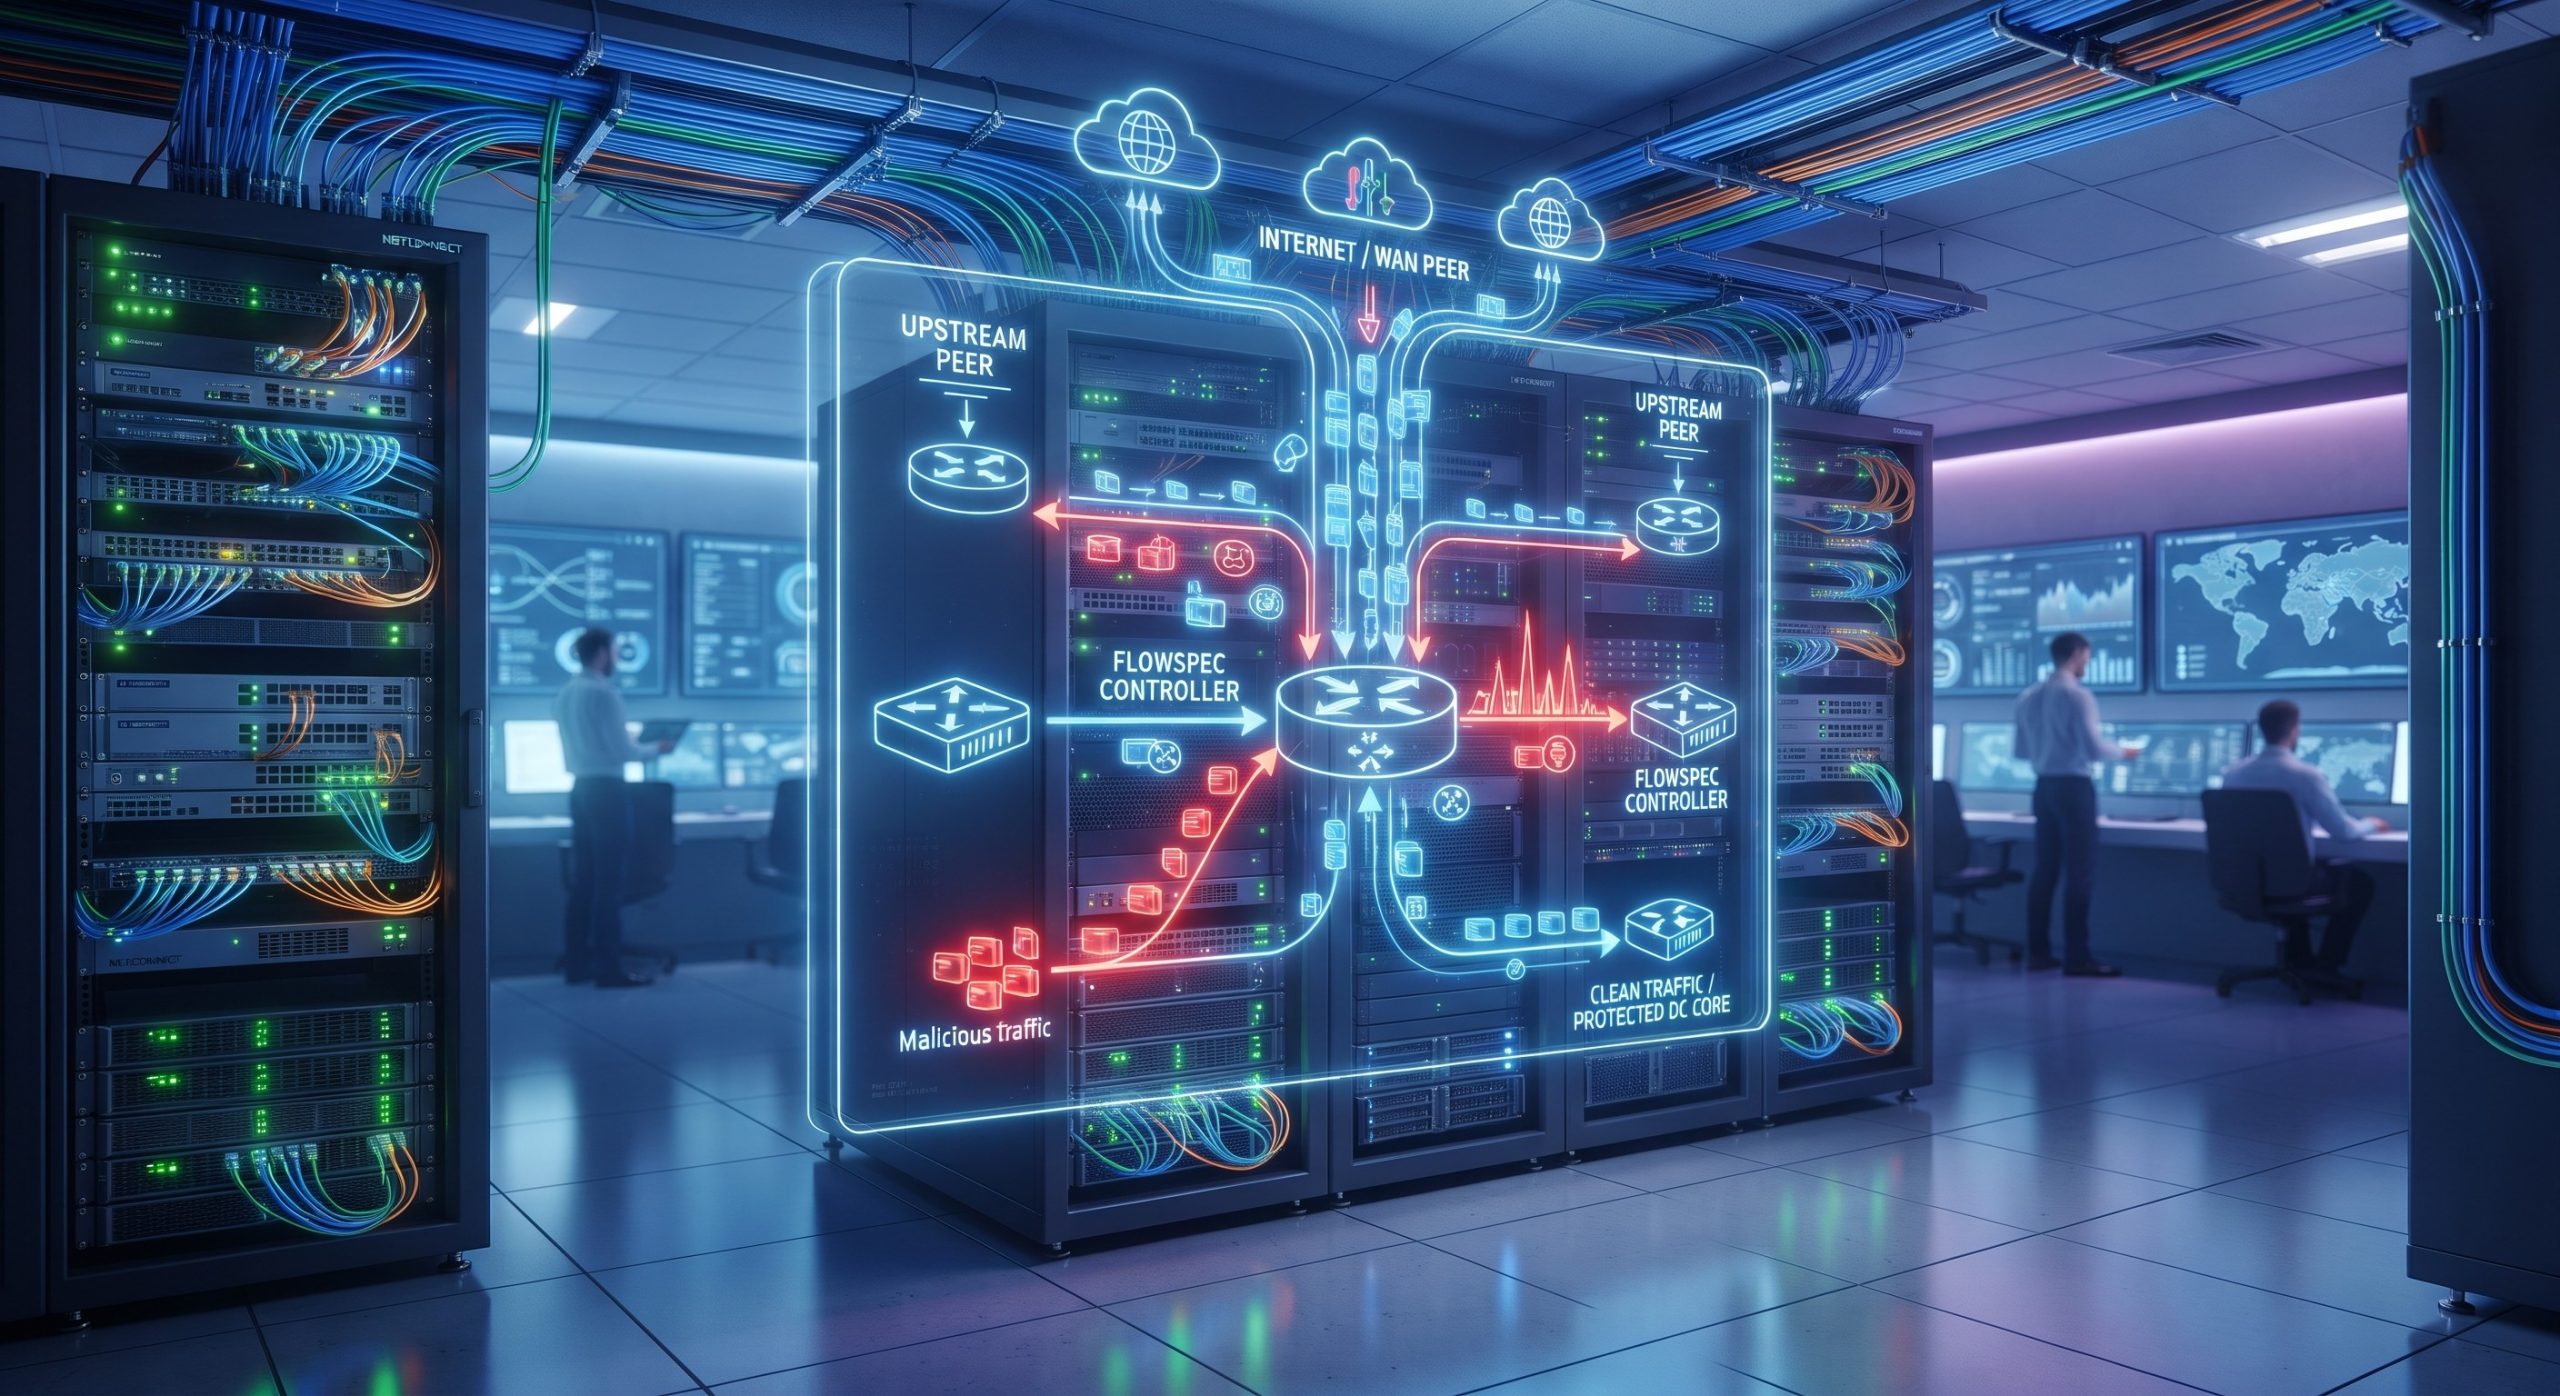
Dual-Engine Failover Architecture and Control-Plane Resilience
Redundant BGP Session Meshing and Route-Reflector Design
The reliability of automated scrubbing hinges on the BGP control plane’s ability to maintain session state during catastrophic traffic events. In a carrier-grade deployment, the FlowSpec Route Reflector (RR) cluster must be geographically dispersed and configured with BGP Graceful Restart (GR) and LLGR (Long-Lived Graceful Restart) helpers. When an edge router’s CPU is stressed by high-volume flow telemetry (sFlow/IPFIX), the BGP session to the FlowSpec controller (e.g., ExaBGP or a dedicated scrubbing orchestrator) must not flap. Field data from inter-AS FlowSpec interoperability labs indicates that improper NLRI decoding can lead to BGP Notification messages and session resets, a scenario that is catastrophic during an active attack . Therefore, the architecture must employ a 1:1 active-standby controller pair with sub-second heartbeats. Upon primary controller failure, the standby must assume FlowSpec NLRI advertisement within < 2 seconds, ensuring that the TCAM (Ternary Content-Addressable Memory) entries on the forwarding ASICs are not prematurely aged out, which would reopen the floodgates to the target.
MTBF Metrics for Scrubbing ASICs and Line Cards
Hardware reliability in the scrubbing path is quantified by the MTBF of the line cards performing the filtering. Unlike standard core routing, FlowSpec enforcement consumes TCAM resources for every unique 5-tuple match rule. A carrier-grade chassis deployed at the scrubbing edge must exhibit an MTBF exceeding 250,000 hours for the fabric modules and 150,000 hours for the line cards under continuous thermal load. Furthermore, the system must support Hitless Forwarding Engine Failover; if the active policy engine (which compiles FlowSpec NLRI into hardware ACLs) crashes, the standby must take over without dropping the existing FlowSpec-installed filters. This is critical because a failover that clears the ACLs would instantly re-expose the victim to the full attack volume, effectively negating the scrubbing infrastructure’s purpose.
| Key Parameter | Technical Specification |
|---|---|
| Protocol Standard | RFC 5575 (obsoleted by RFC 8955); IPv4/IPv6 FlowSpec support required |
| Filtering Actions | Drop, Rate-Limit (bps), Redirect (VRF/RT), DSCP Marking |
| TCAM Rule Capacity | Minimum 4,000 unique FlowSpec entries per line card (carrier-grade) |
| Failover Time (Controller) | |
| MTBF (Line Card) | > 150,000 hours under continuous 40G+ scrubbing load |
| Time-to-Mitigation SLA |
Mission-Critical Deployments: Field Validation and SLA Enforcement
Case Study: Multi-Vector Mitigation Under Load
Real-world validation of FlowSpec reliability is best observed under fire. In a documented incident involving a live cybersecurity training environment, a 48 Gbps multi-vector attack—combining NTP amplification (peaking at 39 Gbps) and a spoofed SYN flood (890,000 packets per second)—was automatically mitigated via FlowSpec injection . The critical reliability metric here is not just the peak throughput, but the time-to-mitigation. The system detected the attack in 0.9 seconds and pushed FlowSpec drop rules to the upstream transit provider within 11 seconds, resulting in zero participant disconnections . This case underscores that when FlowSpec is integrated with per-second telemetry, the SLA (Service Level Agreement) for scrubbing activation can be contractually guaranteed at under 15 seconds for the detection-to-rule-injection phase. For carriers, this reliability must be backstopped by ITU-T Y.1731-compliant performance monitoring to ensure that the scrubbing path itself does not introduce unacceptable latency or jitter for legitimate traffic.
Vendor Interoperability and TCAM Depletion Safeguards
A significant reliability risk in multi-vendor environments is the inconsistent implementation of RFC 5575, particularly regarding Transitivity of Action Communities. The original RFC left certain actions undefined, and interoperability testing revealed that all tested firmwares implemented action communities as transitive, violating the RFC’s explicit non-transitive definition for traffic-rate . In a carrier-grade deployment, this can lead to policy leakage where a rate-limit rule intended for a specific peer is inadvertently propagated across an AS boundary, causing collateral damage. To mitigate this, operators must enforce strict BGP import/export policies on FlowSpec NLRIs and deploy TCAM utilization alarms at 80% capacity. As rule complexity increases (e.g., matching on fragment flags or multiple port ranges), TCAM consumption grows non-linearly. A resilient architecture must support FlowSpec rule compression and priority-based eviction, ensuring that high-priority drop rules for active attacks are never displaced by lower-priority rate-limit rules during a TCAM exhaustion event.
Final Assessment: Engineering Redundancy into Surgical Mitigation
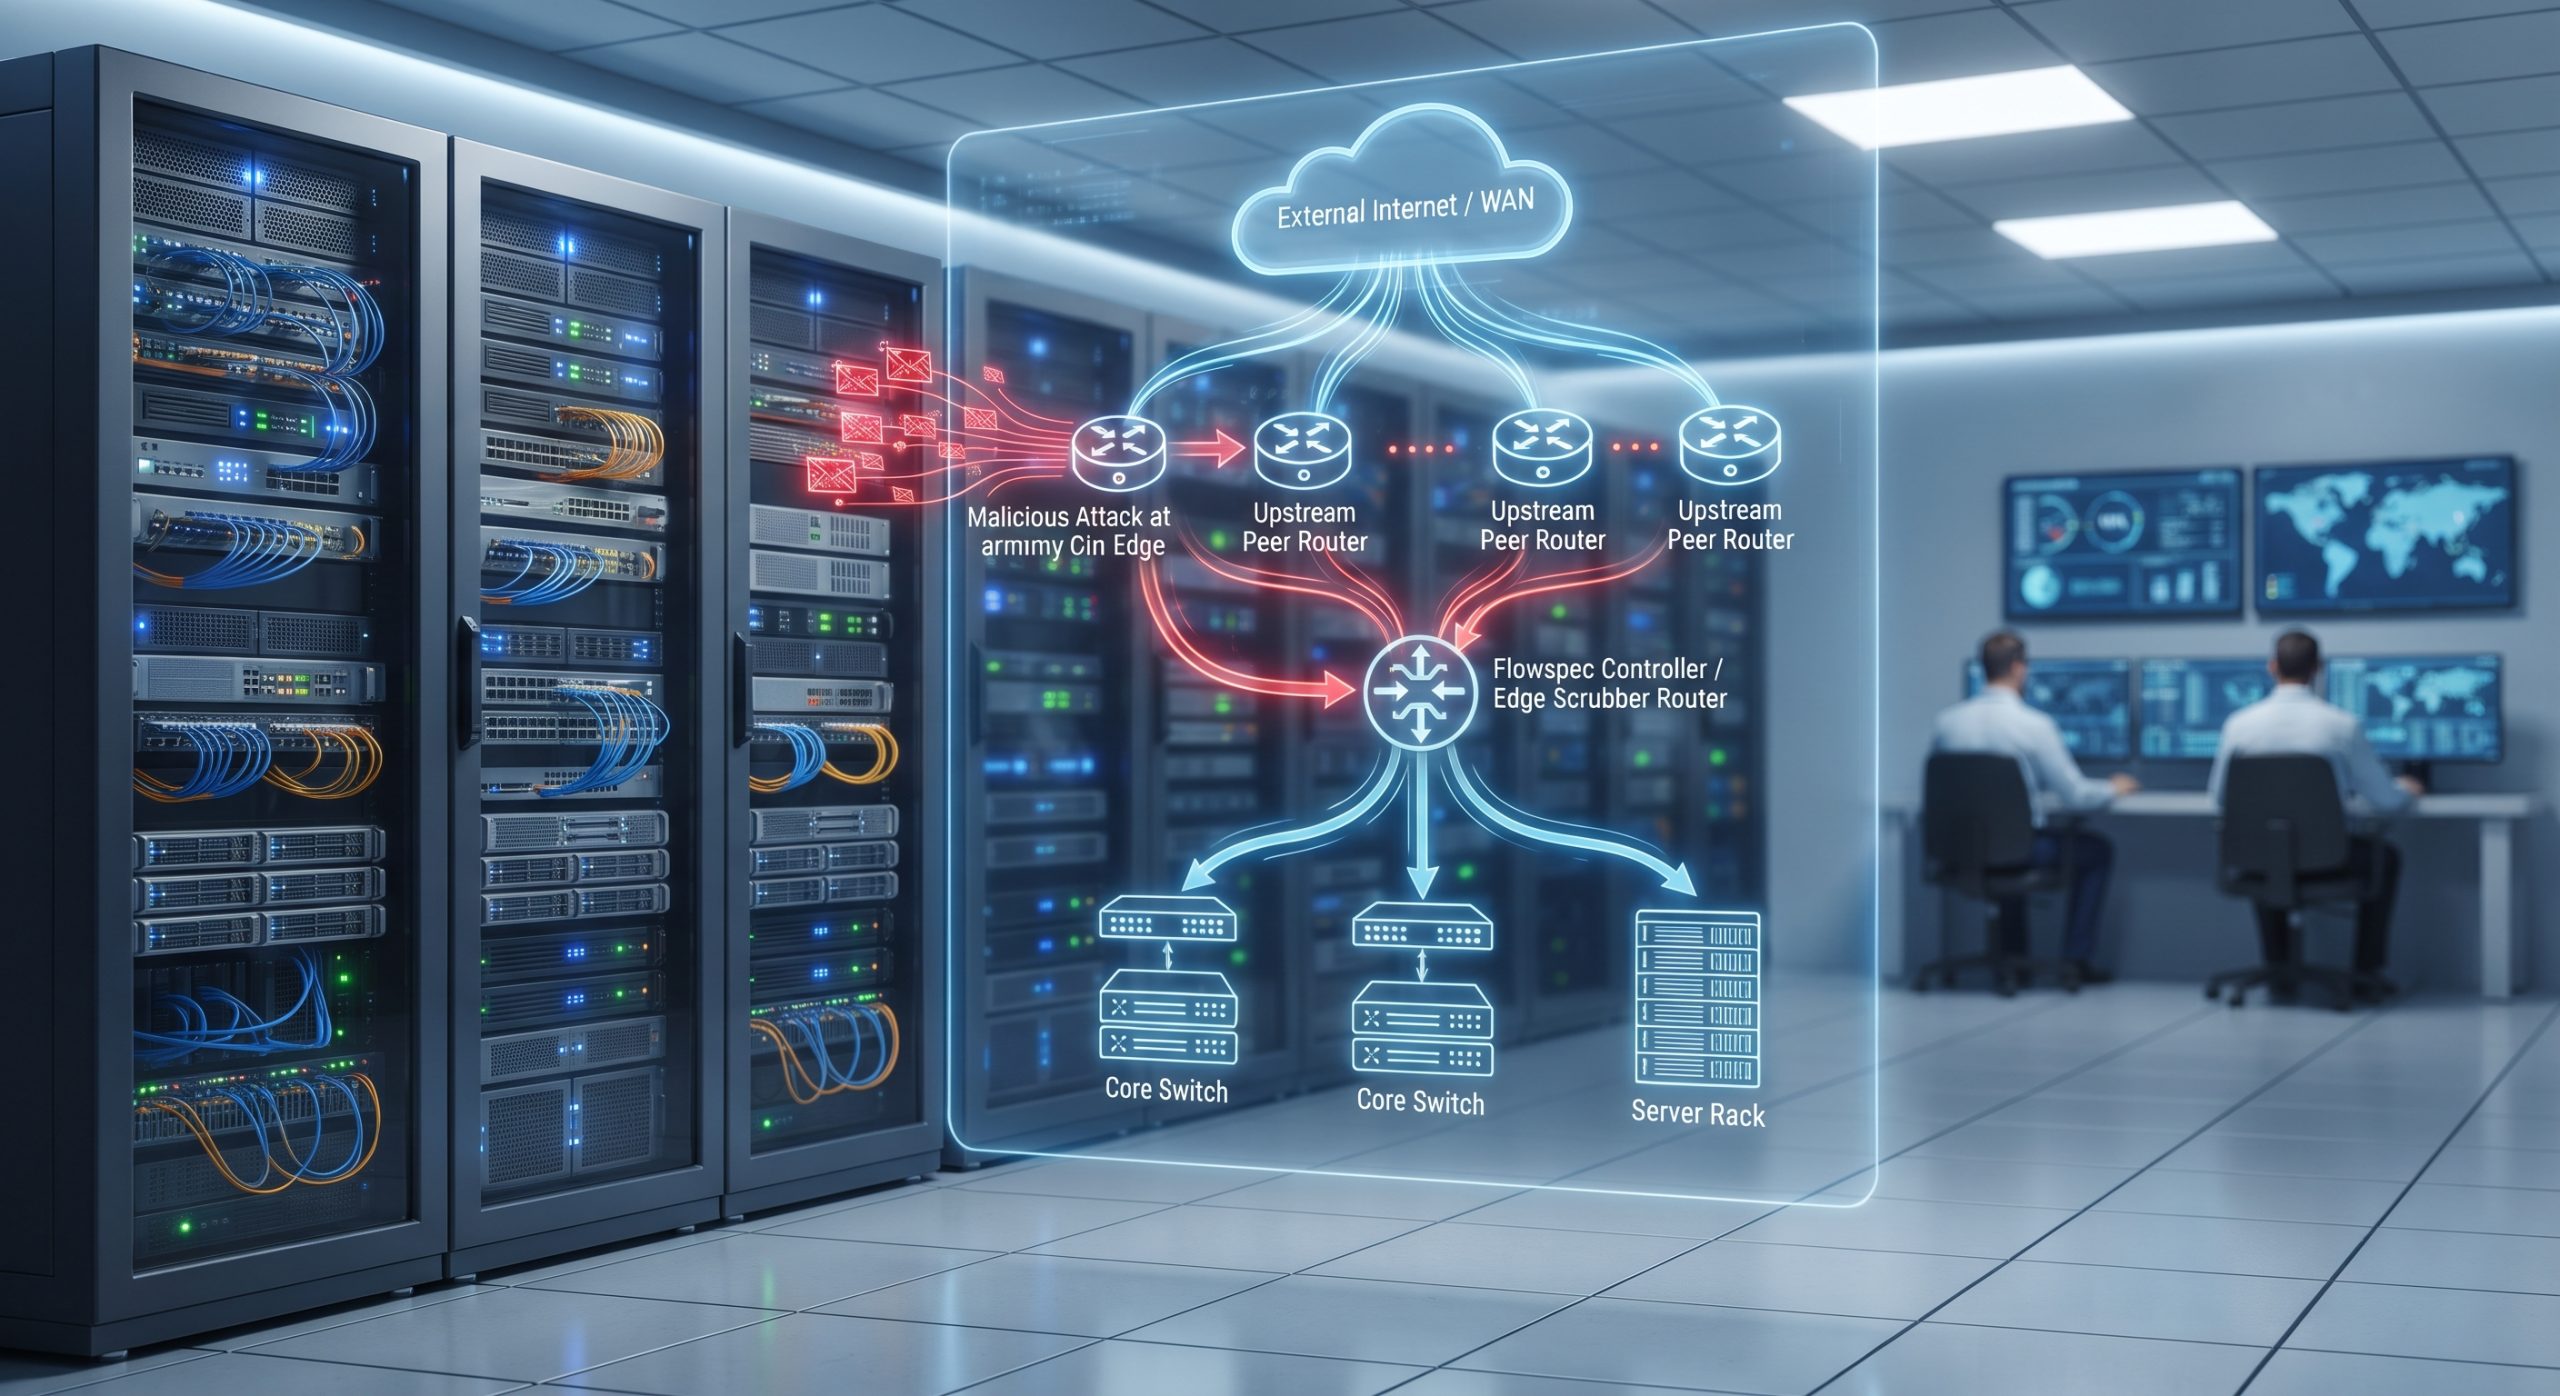
The deployment of BGP Flowspec (RFC 5575) for automated edge scrubbing represents a paradigm shift from reactive blackholing to proactive, surgical defense. However, the reliability of this architecture is not inherent to the protocol; it is engineered through disciplined redundancy. From the MTBF of the ASIC silicon to the sub-second failover of the BGP controllers, every component must be validated against carrier-grade Five Nines standards. As DDoS attacks continue to escalate in volume and sophistication, the network architect’s mandate is clear: implement FlowSpec not as a standalone feature, but as a hardened, dual-engine subsystem that can withstand both the attacker’s traffic and the inevitable failure of individual components. Only then can the promise of precise, automated mitigation be fully realized without introducing a new single point of failure into the core.

Leave a comment