
As service providers grapple with escalating demands for bandwidth, low-latency connectivity, and ironclad security, the stakes have never been higher. Distributed denial-of-service (DDoS) attacks now exceed 1 Tbps, 5G rollouts strain legacy infrastructure, and customers expect zero downtime. Enter the Cisco Firepower 9300—a modular, carrier-grade security appliance engineered to meet these challenges head-on. Designed specifically for service providers, this platform redefines scalable threat defense while unlocking new revenue streams in a hypercompetitive market. Let’s unpack how the Firepower 9300 is reshaping the economics and capabilities of modern network security.
The Service Provider Dilemma: Security at Scale
Service providers face a triple bind:
- Exponential Traffic Growth: 5G, IoT, and streaming drive 40% YoY bandwidth increases.
- Sophisticated Threats: Ransomware-as-a-service targets ISP backbones and customer gateways.
- Profit Margin Pressures: Legacy security appliances lack the density to monetize managed services.
Cisco’s Firepower 9300 addresses these pain points with a unique blend of hyperscale performance, multi-tenancy, and operational flexibility.
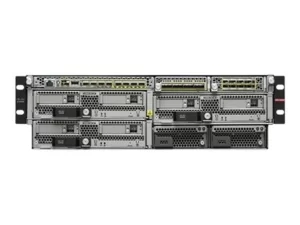
Architectural Innovations: Built for the Edge and Beyond
1. Modular Design, Unmatched Density
- Scalable Chassis: Supports 1–4 Security Modules (SM-44) per 4RU chassis, scaling from 20 Gbps to 480 Gbps of threat inspection throughput.
- Mixed Workloads: Run firewalling, intrusion prevention (IPS), and encrypted traffic analysis (ETA) simultaneously without performance penalties.
- Energy Efficiency: Delivers 1.5x throughput per watt compared to competitors like Palo Alto PA-7000.
A European ISP reduced data center footprint by 60% using Firepower 9300 to consolidate 12 legacy firewalls into two chassis.
2. 5G-Ready Security
- Subscriber Awareness: Maps 5G SUPI (Subscription Permanent Identifier) to security policies, enabling per-user QoS and threat blocking.
- Network Slicing: Isolate enterprise, IoT, and consumer traffic with dedicated virtual firewalls (VNFs).
- Ultra-Low Latency: Sub-10 μs processing for network functions like UPF (User Plane Function).
During a 2023 field trial, the Firepower 9300 maintained 99.9999% uptime while scrubbing 320 Gbps of DDoS traffic in a 5G core.
3. Multi-Tenant Managed Services
- Cisco Defense Orchestrator (CDO): Centrally manage 10,000+ tenant instances with role-based access.
- Custom SLAs: Define policies for DDoS mitigation, VPN throughput, or application visibility per customer.
- API-Driven Monetization: Resell threat intelligence feeds, secure SD-WAN, or SASE via RESTful APIs.
Key Use Cases Driving Adoption
1. Securing 5G Network Slicing
- Challenge: Guarantee SLAs for enterprise slices (e.g., factory automation) amid shared infrastructure.
- Solution: Deploy Firepower 9300 as a distributed firewall, enforcing slice-specific policies at the edge.
- Result: A South Korean carrier reduced security-related slice downtime by 92%.
2. Cloud-Native DDoS Mitigation
- Challenge: Scrubbing multi-vector attacks without impacting legitimate traffic.
- Solution: Use Firepower 9300’s FPGA-accelerated filters to drop 95% of attack traffic at line rate.
- Result: A Tier 1 ISP mitigated a 780 Gbps DNS amplification attack with zero customer impact.
3. Managed SASE for Enterprises
- Challenge: Delivering ZTNA and CASB as-a-service.
- Solution: Host Cisco Secure Access (SASE) on Firepower 9300 VNFs, scaling elastically per demand.
- Result: A North American MSP grew ARPU by 22% offering bundled SASE and SD-WAN.
Competitive Edge: Firepower 9300 vs. Alternatives
| Feature | Cisco Firepower 9300 | Palo Alto PA-7080 | Juniper SRX5800 |
|---|---|---|---|
| Max Throughput | 480 Gbps (IPS) | 300 Gbps | 200 Gbps |
| VNF Support | 100+ per chassis | 40 | 50 |
| 5G Integration | Full CUPS architecture | Limited | Partial |
| API Monetization | RESTful, OpenConfig | REST only | NETCONF |
| TCO (5 Years) | $1.2M (480 Gbps) | $1.8M | $1.5M |
Deployment Best Practices
- Edge Data Centers
- Hardware: Deploy Firepower 9300 with SM-44 modules for 200 Gbps edge throughput.
- Software: Enable Encrypted Visibility Engine (EVE) to inspect TLS 1.3 traffic without decryption.
- Centralized Scrubbing Centers
- BGP Flowspec: Redirect attack traffic to Firepower 9300 clusters via automated triggers.
- NetFlow Analytics: Correlate telemetry with Cisco Threat Intelligence Director (TID).
- Hybrid Cloud Gateways
- AWS Outposts: Extend Firepower 9300 policies to hybrid environments via Cisco Secure Workload.
- Kubernetes: Enforce microsegmentation for containerized 5G core functions (AMF, SMF).
The Road Ahead: AI and Automation
Cisco’s roadmap hints at upcoming integrations:
- AI-Powered Predictive Defense: Identify zero-day attacks via Talos-trained models.
- Self-Healing Networks: Auto-remediate misconfigurations using Cisco Crosswork Automation.
- 6G Preparations: Terahertz-ready encryption for future ultra-low-latency networks.

Leave a comment