PRODUCT IDENTIFICATION
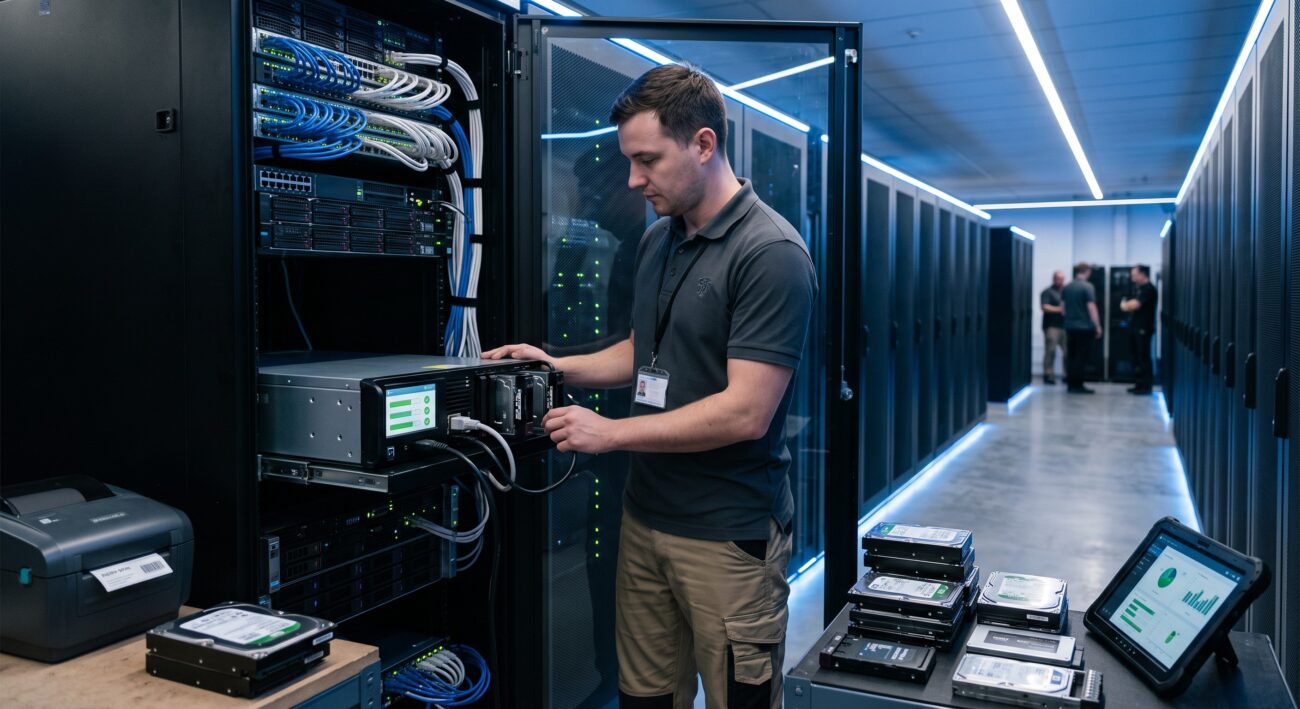
This document establishes the authoritative technical framework for IT Asset Disposition (ITAD) and Data Erasure Standards within carrier-grade telecommunications infrastructure environments. As network operators transition to next-generation architectures, the secure decommissioning of compute, routing, and switching assets becomes a critical operational discipline. This reference manual defines the hardware-agnostic specifications, sanitization methodologies, and compliance mandates governing the lifecycle termination of telecom-grade equipment. The scope encompasses physical destruction protocols, cryptographic erasure techniques, and verifiable audit trails required for regulatory adherence in multi-tenant and hyperscale deployments.
SYSTEM HARDWARE TOPOLOGY
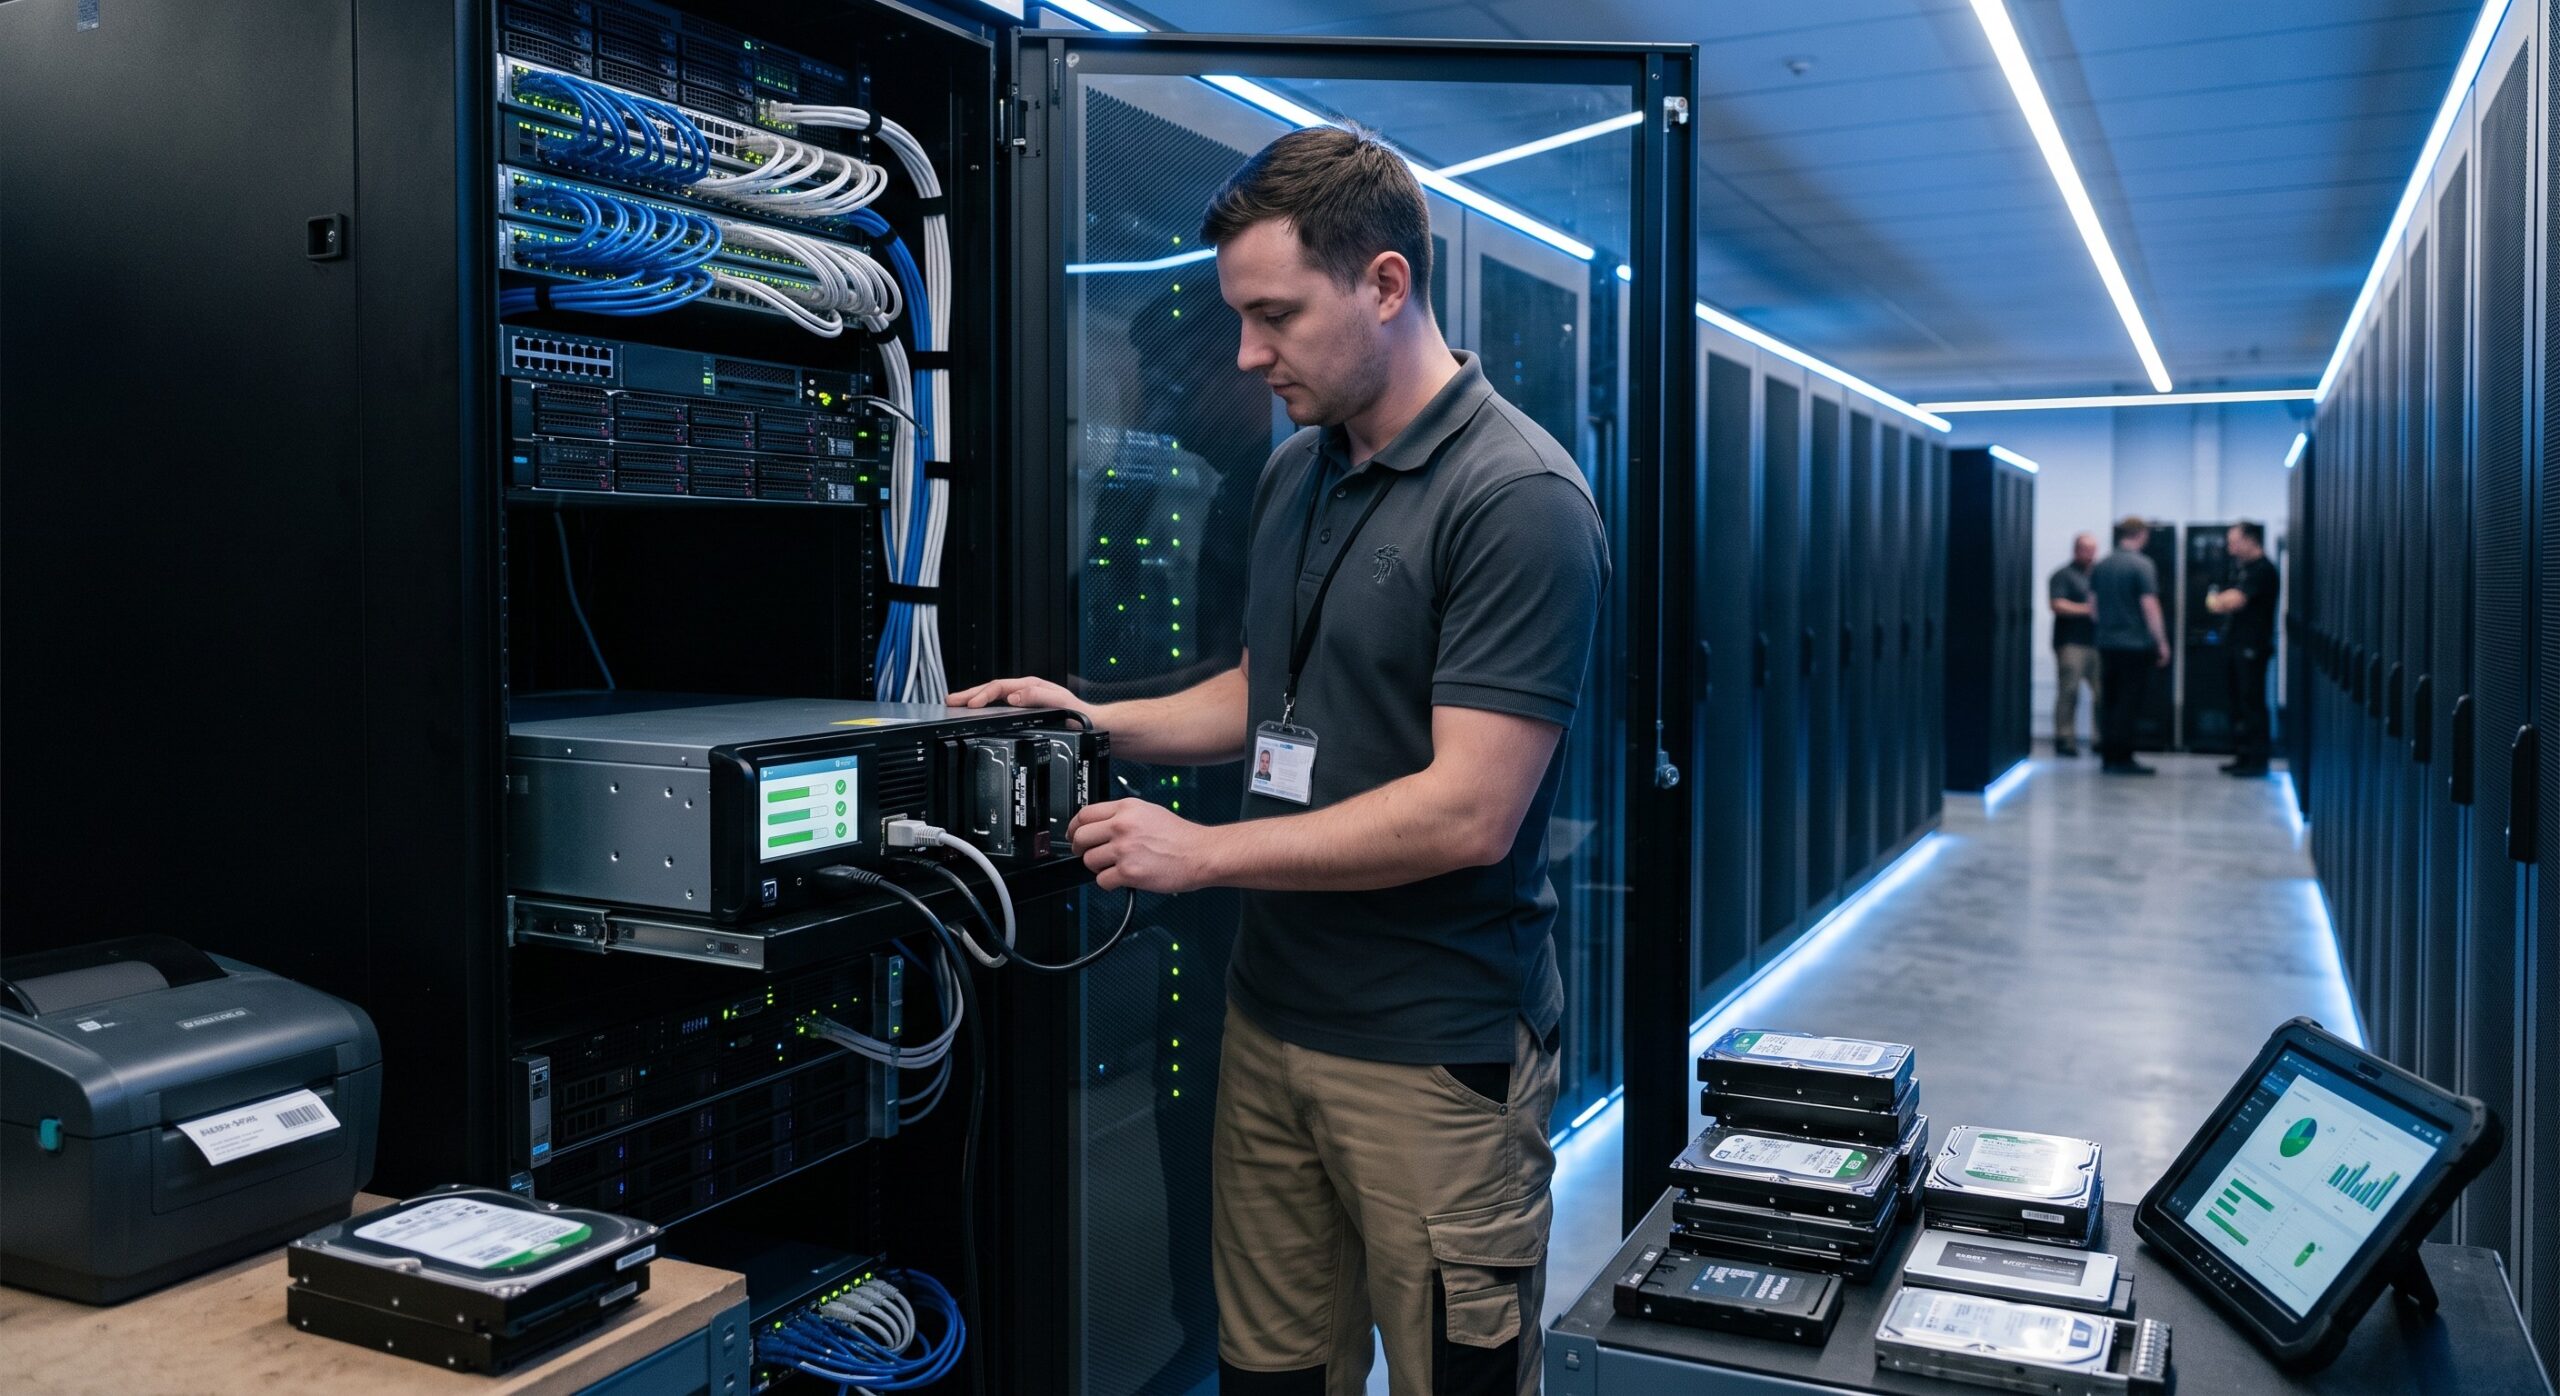
The ITAD process topology integrates directly with existing network management systems (NMS) and element management systems (EMS). Each decommissioned asset—whether a core router line card, optical transport shelf, or edge compute node—must be tracked through a centralized Asset Disposition Engine (ADE). The ADE interfaces with hardware Baseboard Management Controllers (BMCs), IPMI interfaces, and vendor-specific management planes to initiate sanitization commands. For storage-bearing components, including NVRAM, SSD, and HDD modules, the topology enforces a dual-path verification loop: first at the controller level via ATA Secure Erase or NVMe Format NVM commands, and second at the device level through cryptographic hash validation of the erased sectors.
DATA & CONTROL PLANE CAPABILITIES
The control plane orchestrates erasure workflows through policy-driven automation. Operators define disposition profiles based on data classification tiers (e.g., Public, Internal, Confidential, Restricted). The data plane executes the actual sanitization operations across three distinct layers. Layer 1 involves logical overwrite with pseudo-random patterns compliant with NIST SP 800-88 Rev. 1 Purge standards. Layer 2 employs cryptographic erasure (Crypto Erase) by destroying or rotating the Media Encryption Key (MEK) within the self-encrypting drive (SED) controller. Layer 3 provides physical destruction verification via witnessed shredding or degaussing for assets classified as Beyond Economical Repair (BER) or those failing logical sanitization. All control plane actions generate immutable syslog and SNMP trap records.
COMPONENT BREAKDOWN
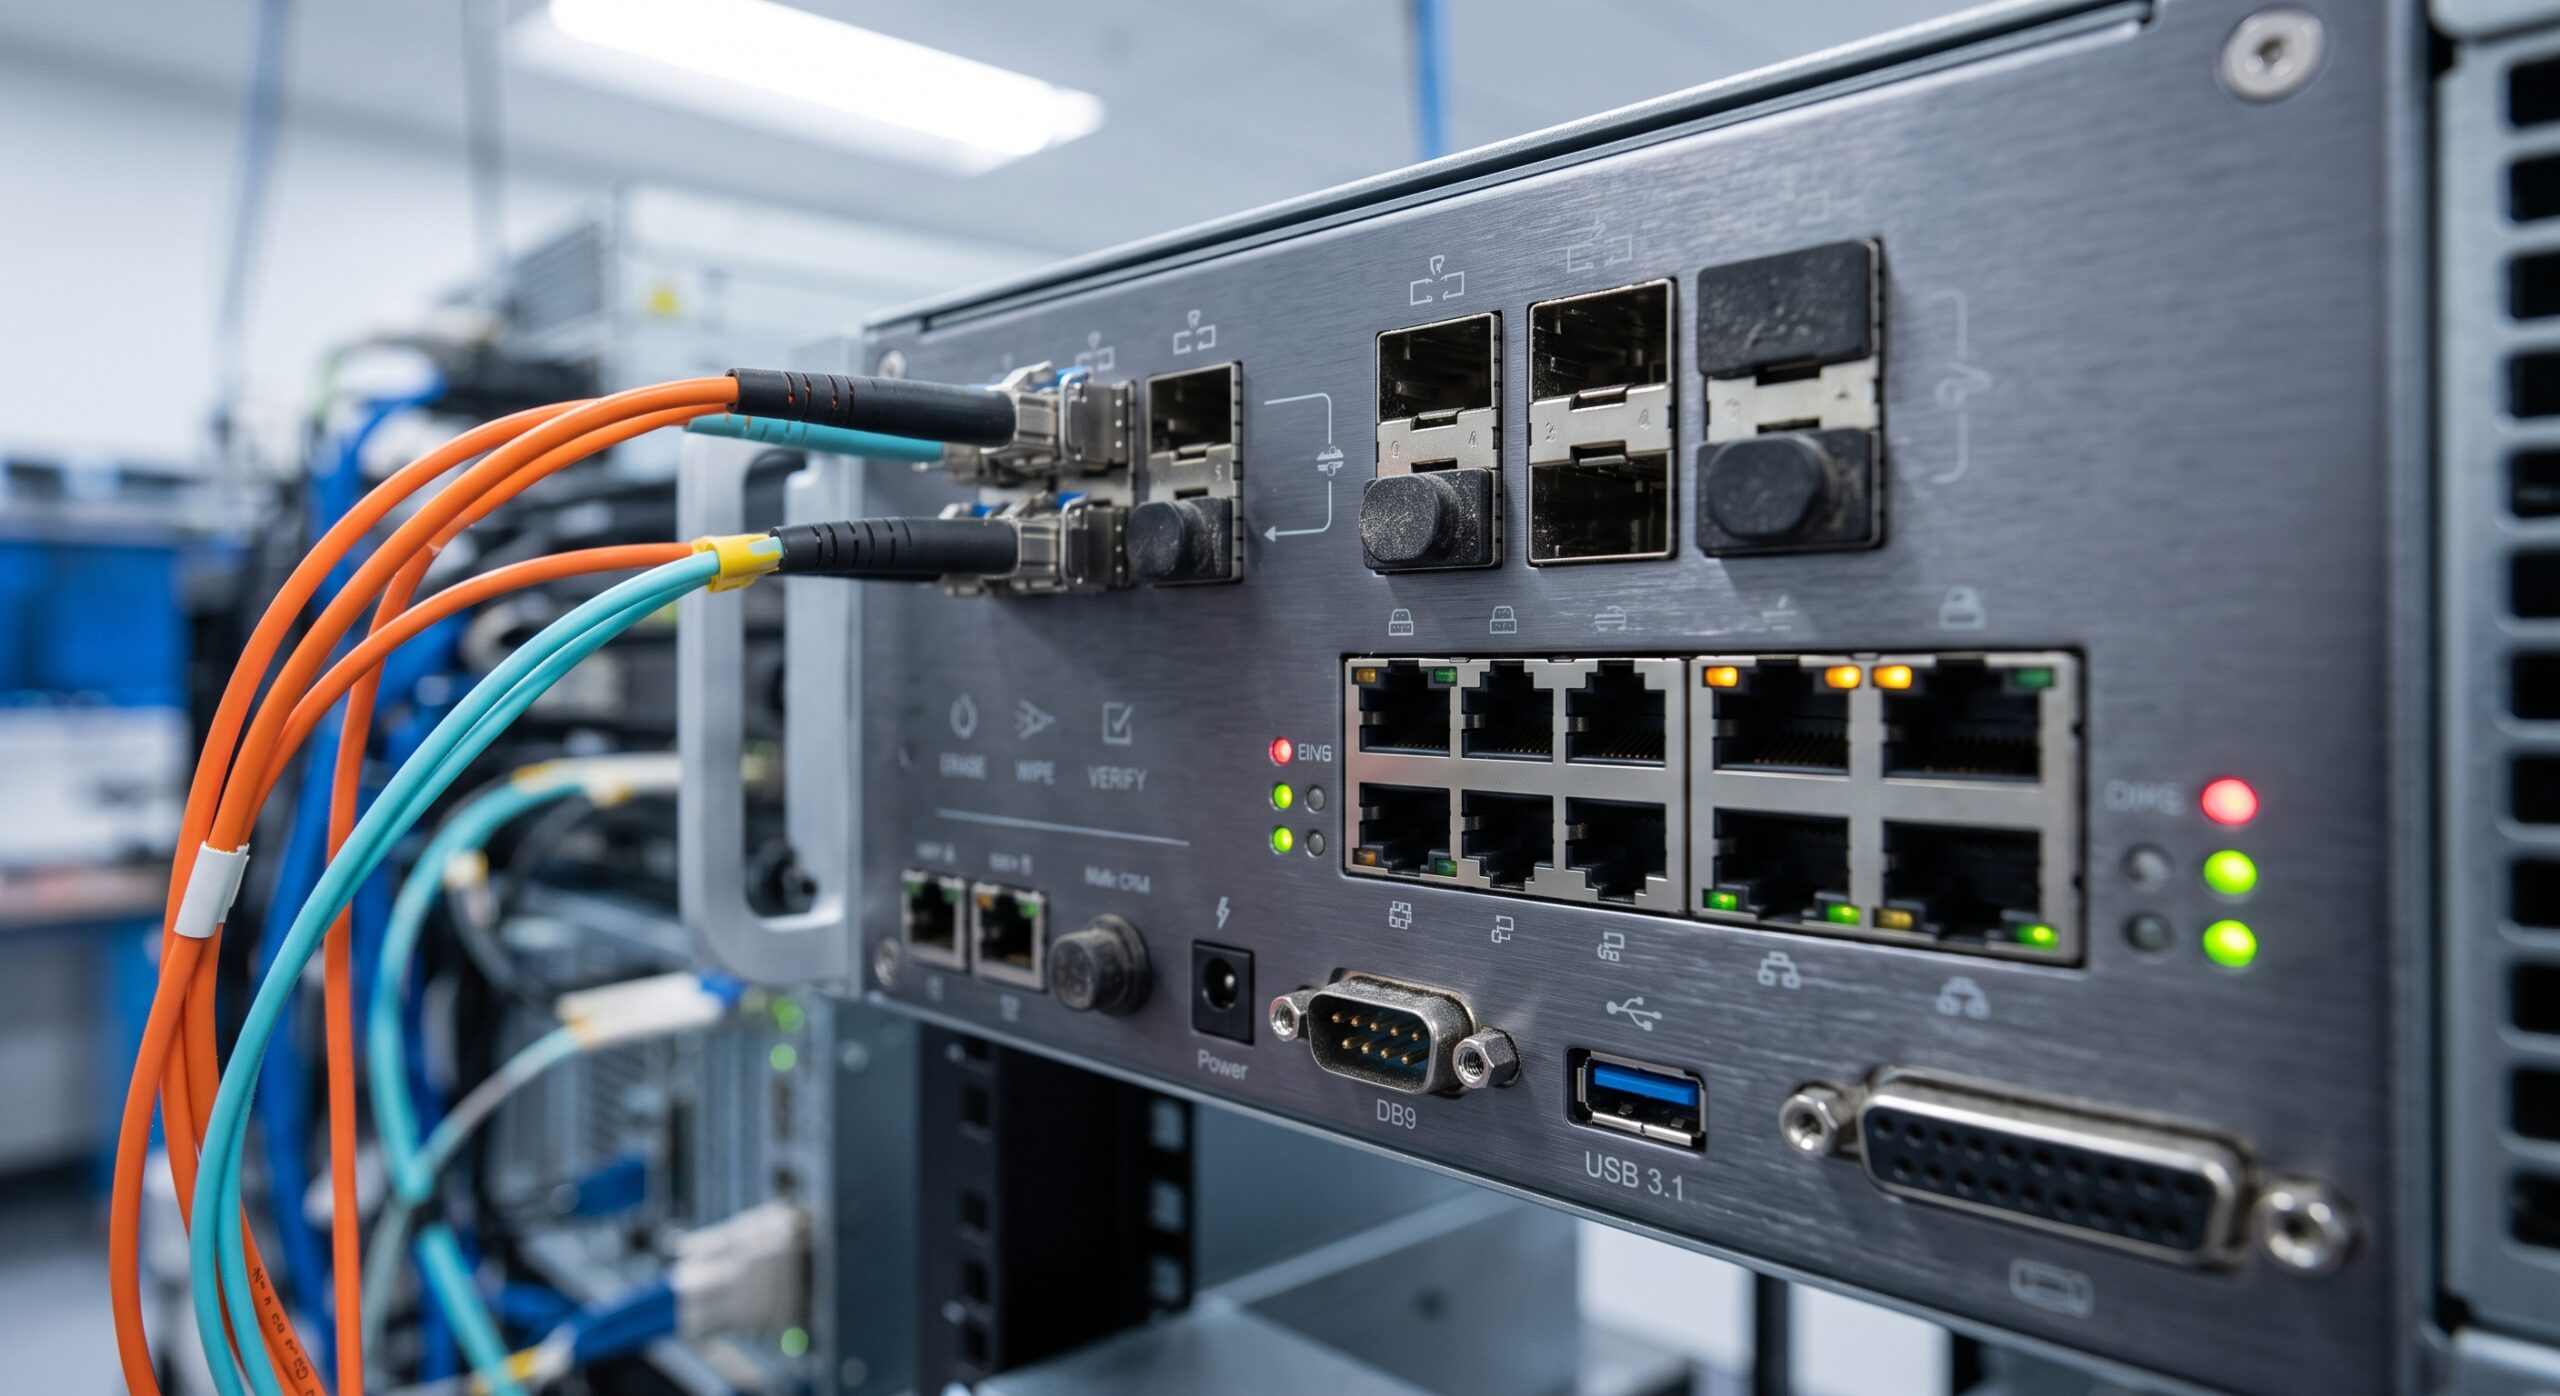
The ITAD hardware ecosystem comprises four functional modules. The Asset Intake Module includes barcode/RFID scanners and optical character recognition (OCR) cameras for serial number and MAC address capture. The Sanitization Appliance is a ruggedized 1RU/2RU chassis housing multi-port SATA, SAS, and NVMe docking bays with hardware write-blockers. The Verification Node performs post-erasure read sweeps using high-speed protocol analyzers. The Destruction Module encompasses NSA/CSS EPL-listed shredders (particle size ≤ 2mm) and degaussers meeting NSA 06-01E specifications. Each module supports hot-swap redundancy and operates within a -5°C to 55°C thermal envelope.
OPERATIONAL SPECS MATRIX
Key operational parameters include a maximum concurrent erasure throughput of 128 drives per appliance, with a sustained data sanitization rate of 12 GB/s per NVMe bay. The system supports over 40 erasure standards including IEEE 2883-2022, NIST SP 800-88 Rev. 1, DoD 5220.22-M, and GDPR Article 17 compliance mappings. Audit log retention is configurable from 90 days to 10 years, with cryptographic sealing using SHA-384. Mean Time Between Failures (MTBF) for the sanitization appliance is calculated at 250,000 hours. Power consumption is rated at 650W typical, with 1+1 redundant AC/DC power supplies.
| Parameter | Specification |
|---|---|
| Form Factor | 1RU / 2RU Chassis |
| Concurrent Drive Sanitization | 128 drives per appliance |
| Sustained Sanitization Rate | 12 GB/s per NVMe bay |
| Supported Erasure Standards | IEEE 2883-2022, NIST SP 800-88 Rev. 1, DoD 5220.22-M, GDPR Art. 17 |
| Cryptographic Erasure | MEK destruction/rotation for SEDs |
| Physical Destruction | NSA/CSS EPL shredders (≤2mm), NSA 06-01E degaussers |
| Audit Log Retention | 90 days to 10 years, SHA-384 sealed |
| MTBF | 250,000 hours |
| Power Supply | 1+1 Redundant AC/DC, 650W typical |
| Operating Temperature | -5°C to 55°C |
REGULATORY COMPLIANCE
This framework adheres to a comprehensive regulatory matrix. Data protection mandates include GDPR (EU) 2016/679, CCPA/CPRA (California), PIPEDA (Canada), and LGPD (Brazil). Industry-specific standards encompass HIPAA (healthcare), PCI DSS v4.0 (financial), and SOX (corporate governance). Hardware and environmental compliance includes WEEE Directive 2012/19/EU, RoHS 2011/65/EU, and ISO 14001:2015 for environmental management. Security certifications include ISO/IEC 27001:2022, SOC 2 Type II, and Common Criteria EAL4+. For telecommunications-specific requirements, the framework aligns with ITU-T X.805 security architecture and 3GPP TS 33.210 for network domain security.
📥 Download Technical Specification
Click the button below to view or download the full official PDF datasheet.
Leave a comment